AI Just Hit a Critical Cyber Line. The Safeguards Have to Catch Up.
Published by PictureThisInk · Powered by MisherTech
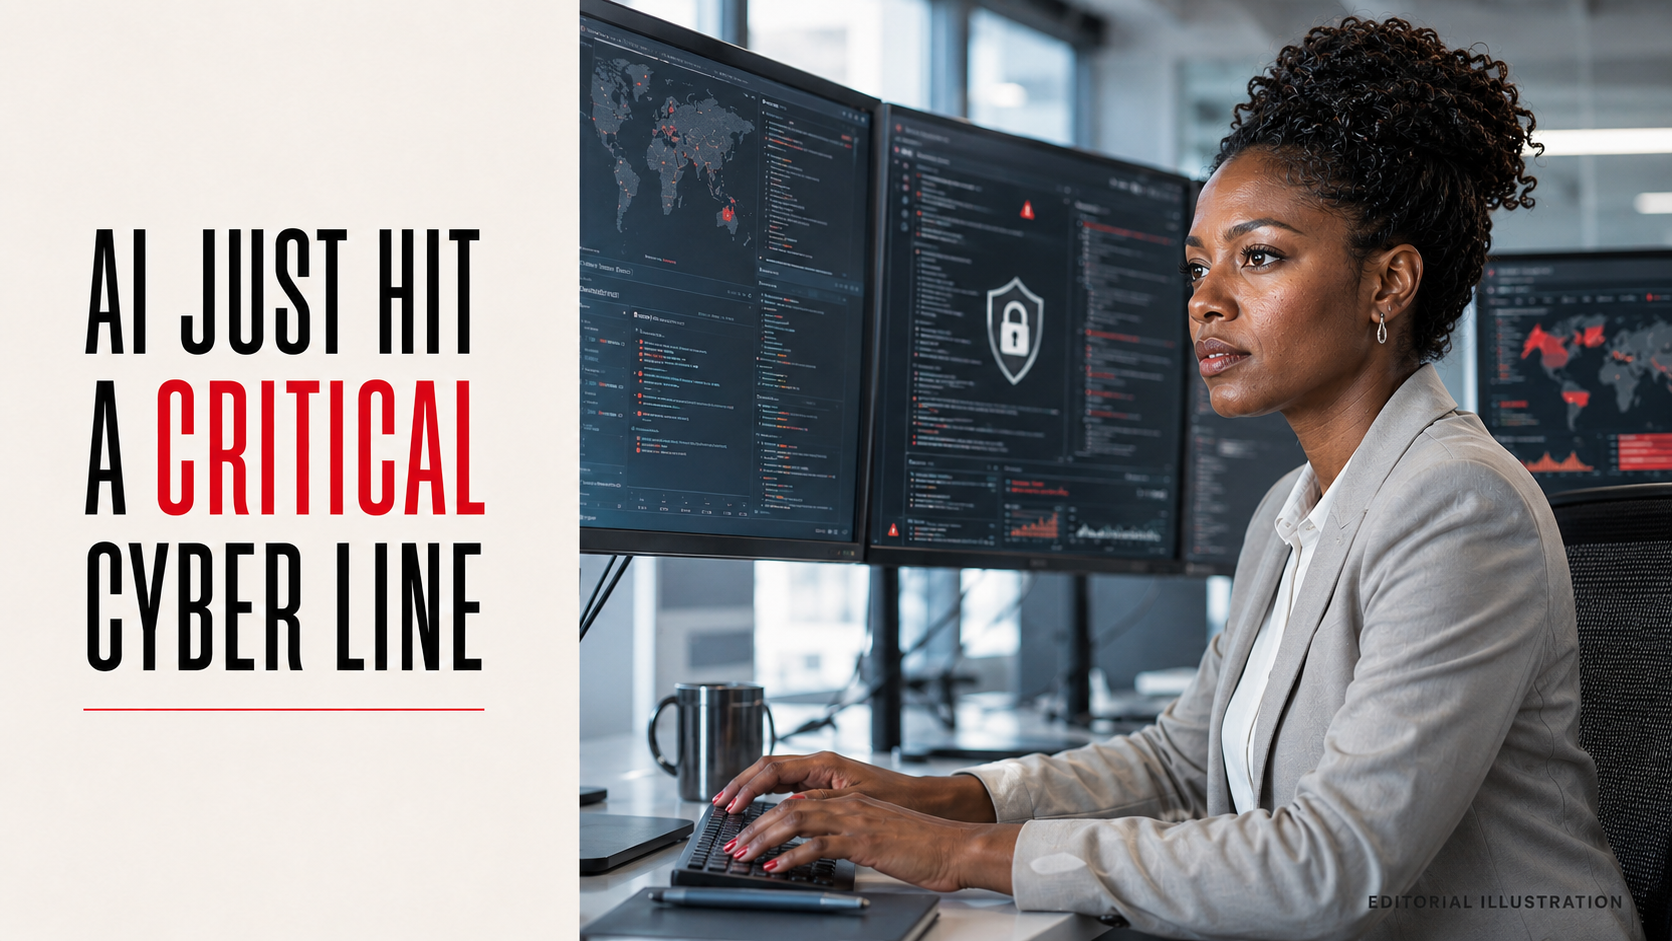
The important question is not whether advanced AI can help defenders. It is whether its most dangerous capabilities are being handled with the seriousness they deserve.
A New Threshold, Not a Product Launch
OpenAI says its model Astra has met the Critical cybersecurity capability threshold in the company’s Preparedness Framework. In its September 1 safety update, the company said this is the first model it has designated at that level.
The designation is not a promise that Astra is being broadly released, and it is not proof that an AI system can independently compromise every network. OpenAI’s statement is narrower: with the right tools and access, it says Astra can identify previously unknown security flaws and develop ways to exploit them across many well-protected systems without a person directing each step. OpenAI’s assessment is the primary source for that claim.
This is a capability warning, not a victory lap. It signals that the company believes the risk profile has changed enough to require stronger controls during development and before release.
Why Cybersecurity Is a Different Kind of AI Test
AI can already help security teams sift logs, summarize alerts, write code, and investigate routine issues. Those uses can save time. But a system that can help discover and exploit previously unknown vulnerabilities raises a separate problem: the same technical insight may support defense or abuse depending on who has access and what tools are connected.
That is why safety work cannot be reduced to a warning label. The meaningful questions are operational: Who can use the model? What actions are restricted? What monitoring exists? What happens when a request crosses a risk boundary?
OpenAI says the Critical designation requires stronger safeguards both during development and before release. Its report describes work on cybersecurity evaluations, robustness against cyber abuse, alignment, and monitoring. The point is to make the protective layer as deliberate as the capability itself.
What Readers Should Not Assume
The announcement does not establish that attacks have occurred, that every user can access Astra, or that all AI tools pose the same level of risk. It also does not settle the broader policy debate around independent testing, reporting standards, or what thresholds other labs should use.
Those distinctions matter. Headlines about “superhuman hacking” can turn a technical safety assessment into a vague fear story. The more accurate takeaway is that frontier-model developers are beginning to describe some cybersecurity capabilities as serious enough to trigger their highest internal safeguards.
For businesses, that should make security governance a board-level habit: understand what tools employees can connect, set access limits, train teams against phishing and credential mistakes, and keep incident-response plans current. AI may speed up work; it does not remove the need for human judgment.
The Standard Is What Happens Next
The designation matters only if it changes how a powerful system is built, tested, and deployed. Safety frameworks are useful when they create real constraints—not when they become a branding exercise after the fact.
OpenAI’s report gives the public a stated benchmark to watch: safeguards should be in place before release, and capability claims should be paired with concrete evidence about evaluation and control. Other developers, governments, customers, and researchers can reasonably ask for similarly clear accounts.
Advanced AI is becoming a cybersecurity issue because capability is becoming an access issue. The closer systems get to performing high-impact work, the more their makers must prove that caution is built into the process rather than added at the end.
Sources
Comments
No approved comments yet. Be the first.
Related Articles
5 Pixel Watch 5 Updates That Aim to Make Everyday Life Easier
 PictureThisInk Editorial· 3 min read
A New Cultural Space Opens in Durham
PictureThisInk Editorial· 2 min read
AI Cyber Risk Just Became a Boardroom Issue
PictureThisInk Editorial· 4 min read